
Utilities Windows
Syslog Watcher
Collect syslog messages on Windows, filter network events and forward logs to a SIEM with Syslog Watcher. The included free license covers three originators and 5,000 messages per hour.
- Operating system
- Windows 8.1, 10, 11; Windows Server 2012 R2, 2016, 2019, 2022, 2025 (64-bit)
- Architecture
- 64-bit
- Download package
- MSI installer
Publisher supports physical, virtual and cloud Windows hosts. The 150 MB minimum program-space figure excludes collected syslog storage, which depends on message volume and retention.
Link checked · Download guidance
What is Syslog Watcher?
Syslog Watcher is a Windows syslog server for collecting messages from network devices, servers and applications in one place. It suits administrators who need to review events across several devices rather than inspect each device separately. The publisher lists UDP, TCP and TLS collection, message filtering, search, alerts and reports.
Collected messages can be retained locally, forwarded to another syslog receiver or exported to ODBC, CSV, XML and JSON. Windows Event Log input is listed through the separate EventLog Inspector product; it should not be confused with direct syslog collection.
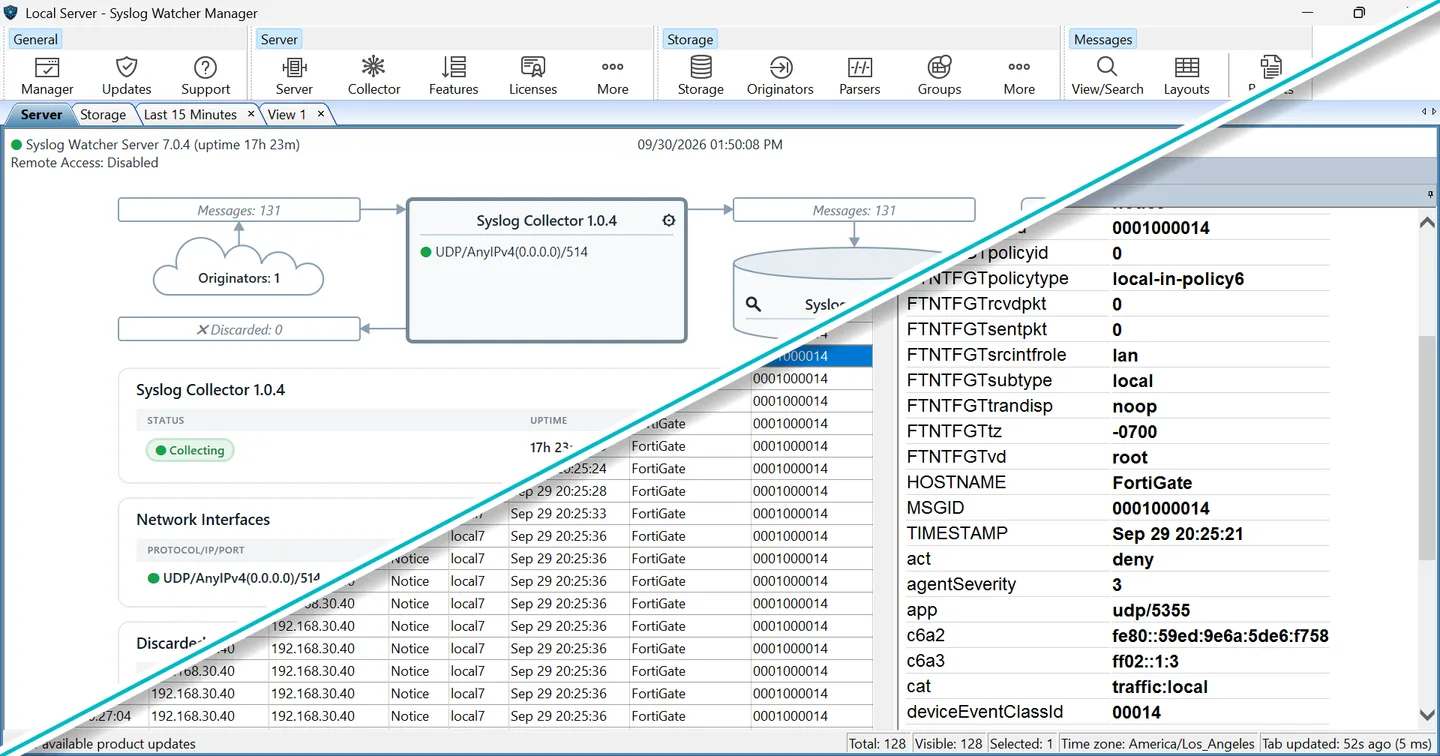
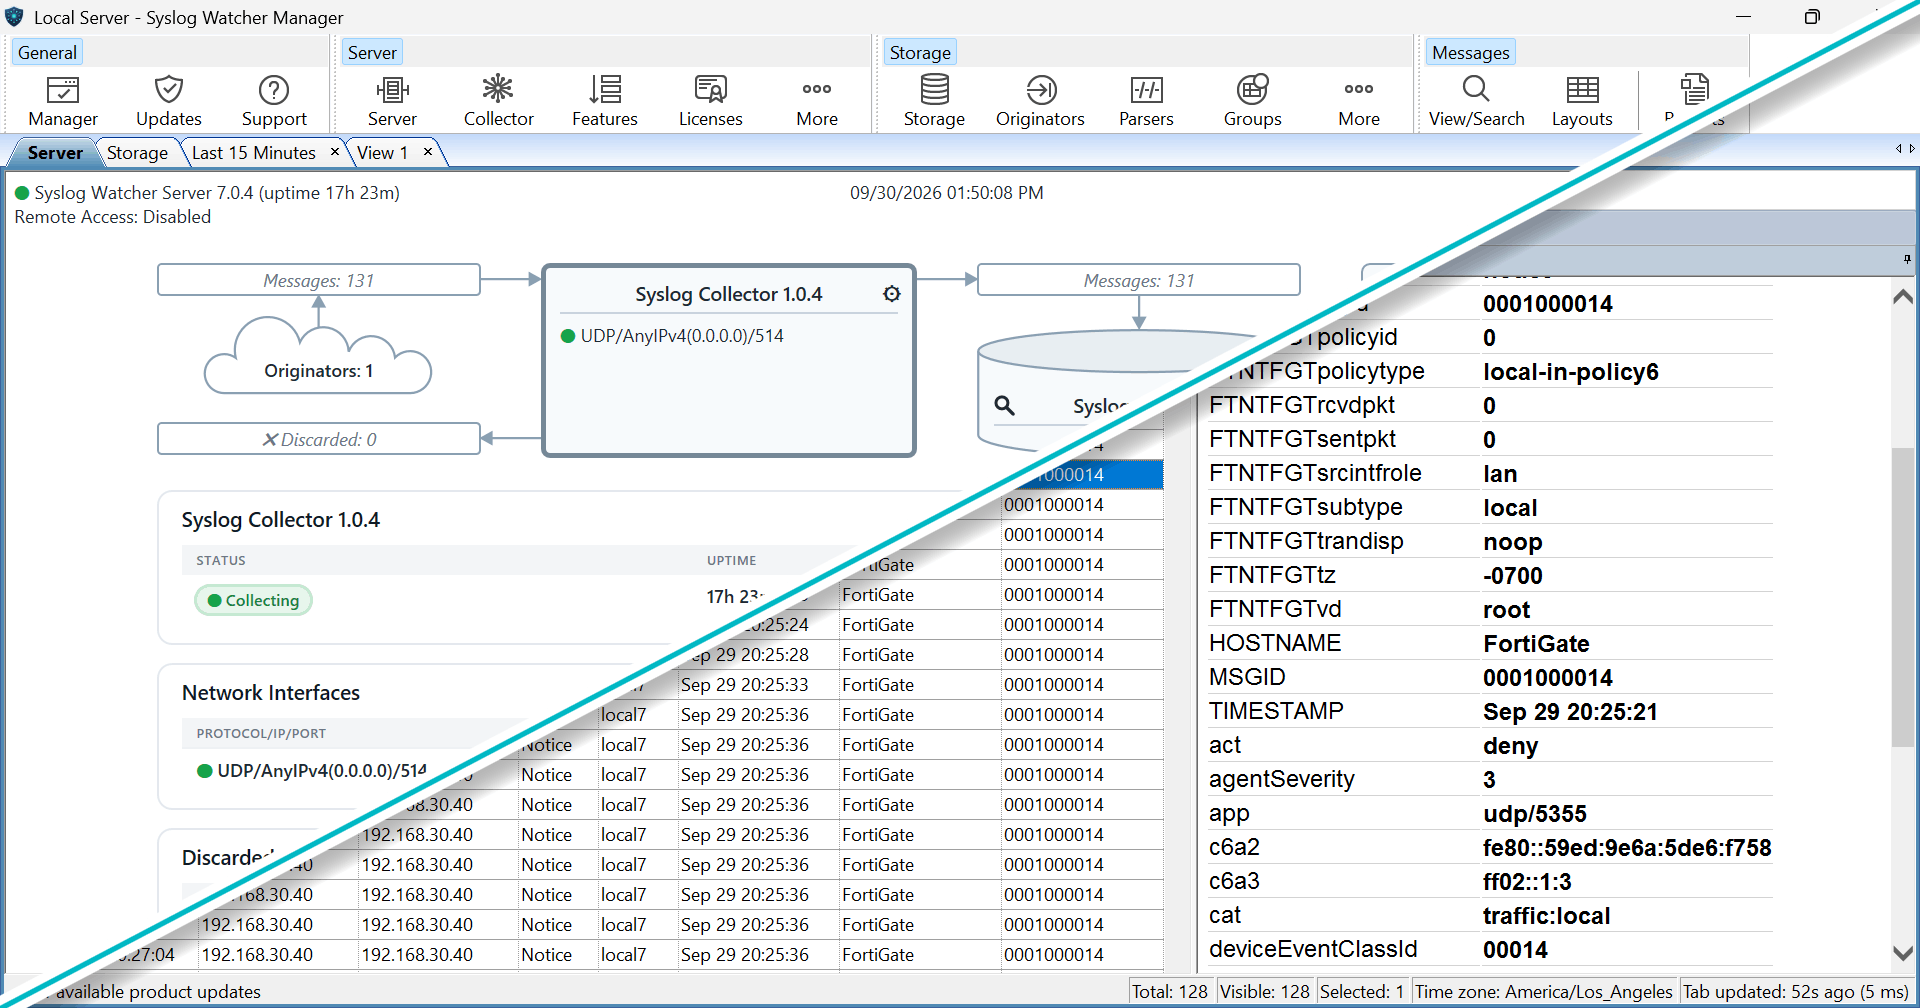
The installer includes a free license limited to three syslog originators and 5,000 messages per hour. A larger deployment needs an appropriate commercial license; the publisher also offers a requested 30-day evaluation of its license types. This entry links to the Windows 64-bit MSI for version 7.0.6. The publisher screenshot illustrates the 7.0 interface and visibly shows server version 7.0.4, not the exact linked build.
What it offers
- Receive syslog messages over UDP, TCP and TLS.
- Filter and search collected messages in a Windows management interface.
- Use alert expressions and syslog reports to review selected events.
- Forward filtered messages to another syslog receiver or SIEM collector.
- Export messages to ODBC, CSV, XML and JSON.
Good to know
- The included free license is limited to three syslog originators and 5,000 messages per hour.
- Windows Event Log forwarding is listed through the separate EventLog Inspector product, rather than as direct Windows Event Log collection in this download.
Product images
Sources
References used for this listing. Retrieval dates do not indicate hands-on testing.
More in utilities
View category ↗System Scheduler 6.00
Schedule programs, batch files and popup reminders with System Scheduler Free for Windows. Its Window Watcher can respond to application windows; running jobs while logged off requires Professional.
Round-Robin Mailer 37.0
Distribute incoming email leads among sales staff in rotation with Round-Robin Mailer for Windows, using staff schedules, availability and weighted allocations.
Fluent Bit 5.1.3
Collect, process and forward logs, metrics and traces with Fluent Bit, an open-source telemetry agent with Windows Event Log inputs and Windows service support.
SysInfo Gmail Attachment Downloader
Save attachments from selected Gmail emails to a local folder using the Windows SysInfo Gmail Backup workflow. The demo covers the first 50 emails per folder.
EventLogExpert 26.8.24.986
Open exported EVTX files, combine logs in time order and monitor live Windows event channels with Microsoft's free, open-source EventLogExpert.